
01My approach
I learn by doing, on intentionally vulnerable and legal environments. One rule: never submit a flag without understanding why it worked. When a challenge really teaches me something, I write it up.
02TryHackMe
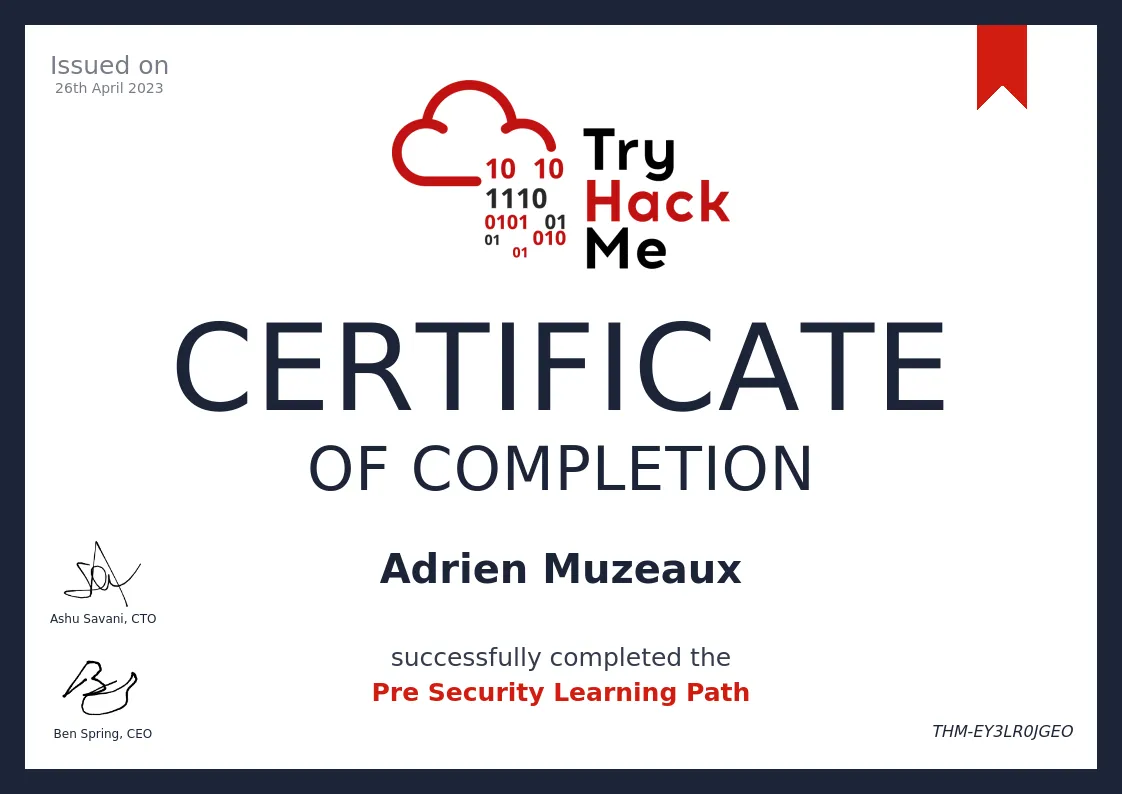
My entry point in 2023. I completed the Pre Security path (networking, Linux, Windows, how the web works), then a long run of pentest rooms. Today: 70 rooms completed, 11 badges, top 5% of players.
03Root-Me
60 challenges solved, mostly web and steganography. The latest ones: CSRF, stored XSS, broken access control on an API.
| Category | Solved |
|---|---|
| Web – Server | 23 |
| Web – Client | 11 |
| Steganography | 11 |
| Cryptanalysis | 7 |
| Network | 5 |
| App – Script | 2 |
| Forensics | 1 |
04Hack The Box: CJCA path
I've started the Hack The Box Academy path leading to the CJCA (Certified Junior Cybersecurity Associate) certification. It deliberately mixes offense and defense: understanding an attack, but also detecting and analyzing it. Goal: sit the exam in early 2027.
05Write-ups
My write-ups are written like real penetration test reports: scope, findings with their CVSS score, methodology, then remediation advice. They are in French.