
Adrien Muzeaux.
Third-year student at ESILV (Paris), currently on exchange at Riga Technical University. I do vulnerability research, CTFs and infrastructure, and I published my first CVE in 2026.
Break things cleanly, understand them deeply
I wrote my first lines of code at 11, in 2017, to build Discord bots in JavaScript. That's where I discovered Node.js, APIs and event-driven logic. Then one thing led to another: modern JavaScript, React to build interfaces, HTML and CSS to polish my sites. In high school I built Wizanimes, a streaming platform in PHP and MySQL with user accounts and an admin panel, then picked up Python to automate tasks and drive a connected CO₂ sensor.
The more I learned to build applications, the more another question caught my interest: how they break. In 2023 I signed up on TryHackMe, then Root-Me, and offensive security became my priority. Today I'm working through Hack The Box's CJCA path.
In 2026, while reading the source code of SVGO, a widely used Node.js library, I found two ways to sneak JavaScript past its security filter. I reported it to the maintainers, a fix shipped, and the issue became CVE-2026-73650. I'm now turning it into a CTF challenge.
At ESILV I'm part of DaVinciCode, the school's cybersecurity club, where I work on the Infrastructure project.
I'm looking for a cybersecurity apprenticeship starting September 2027 for my last two years of engineering school. In France, an apprenticeship (alternance) means alternating between school and a company, under a 2-year work contract.
- SchoolESILV, engineering cycle, year 3
- Class of2029
- ExchangeRiga Technical University, Latvia
- Looking forCyber apprenticeship · Sept. 2027
- Duration2 years (years 4 and 5)
- LanguagesFrench · Fluent English
What I work on
Security projects first. My early web projects are grouped further down, in the archive.
<svg xmlns="…/2000/svg" xmlns:svg="…/2000/svg">
<svg:script>alert(1)</svg:script> // survives the filter
<a href="JavaScript:…"> // case ignored
</svg>
// CVE-2026-73650 · CVSS 8.2 High
CVE-2026-73650: XSS in SVGO
SVGO promises to strip anything that can execute JavaScript from an SVG. I found two ways to get a script through that filter. Reported privately, fixed in 3.3.4 and 4.0.2.
Read the projectservices:
app: # the app cleans SVG logos
bot: # the admin bot visits links
FLAG: DVC{????????}
// status: work in progress
CTF challenge "Presque Propre"
Turning my CVE into an exercise: a fictional platform that cleans user SVG logos, and an admin bot that visits reported links. Your job is to find what the filter lets through.
Read the project
DaVinciCode, Infrastructure project
Operations, improvements and hardening of the servers hosting the club's services and CTF platforms.
Read the project
davincicode.fr, the club's website
The website of DaVinciCode, ESILV's cybersecurity club, designed and built by a team of two from October 2025 to May 2026: from the React front end to deployment behind Nginx and Docker.
Read the projectOffensive training
Top 5% on TryHackMe with 70 rooms, 60 challenges solved on Root-Me, and Hack The Box Academy's CJCA path in progress.
Read the project
Raspberry Pi home lab
A portable cybersecurity lab on a Raspberry Pi 4: a hardened server, intentionally vulnerable apps to train on, and a monitoring dashboard.
Read the project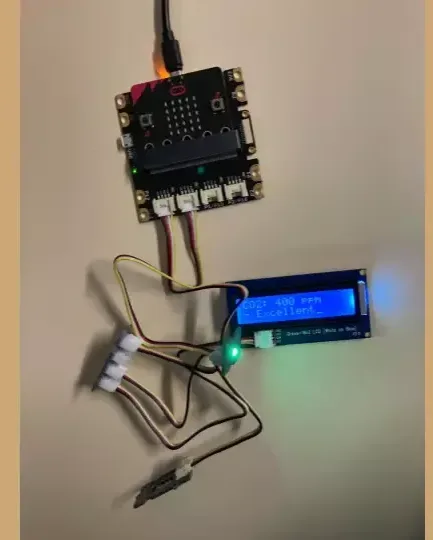
Connected CO₂ sensor
Measure a room's CO₂ and open the window on its own: two micro:bit boards, a sensor, a motor, SysML modeling and a CAD enclosure.
Read the projectArchive: my early web projects 2021 to 2024 · high school
Education & experience
-
Aug 2026 – Jan 2027
Exchange semester · Riga Technical University
Riga, Latvia · Faculty of Computer Science, IT and EnergyTaught entirely in English: machine learning, signal theory, probability and statistics, numerical methods, operations research, data models in database systems, project management.
-
Jul 2026
Coordinated disclosure · CVE-2026-73650
SVGO · open sourceTwo bypasses of the
removeScriptsplugin leading to XSS. Advisory published on 2026-07-11, CVE assigned on 2026-08-13. Read the write-up → -
Oct 2024 – now
Infrastructure project · DaVinciCode
ESILV's cybersecurity club · Courbevoie / hybridClub member since October 2024, on the Infrastructure project since October 2025: operations, improvements and hardening of the servers hosting internal services and CTF platforms. Details →
-
Sep 2024 – 2029
Master's-level engineering degree · ESILV
École Supérieure d'Ingénieurs Léonard de Vinci · Paris-La DéfenseTwo-year integrated preparatory cycle, then the engineering cycle, currently in year 3. Goal: a cybersecurity major, ideally as an apprentice from year 4.
-
2023 – now
Self-directed offensive practice · TryHackMe · Root-Me · Hack The Box
Alongside my studiesTop 5% on TryHackMe with 70 rooms, 60 challenges solved on Root-Me, and now Hack The Box Academy's CJCA path. Details →
-
2017 – 2023
Getting started · Self-taught
Middle & high schoolFirst lines of code at 11 (Discord bots in JavaScript), then HTML/CSS, React, PHP/MySQL and Python. Work-observation placement at IBM at 14, and a connected CO₂ sensor in engineering class.
Certifications & credentials
HTB CJCA, Certified Junior Cybersecurity Associate
Permis d'OSINTeur (OSINT licence)
Design Thinking
Pre Security Learning Path
Codeur Junior Pro, Python
English certification
Toolbox
Offensive security
Networking & analysis
Systems & infrastructure
Development
Languages
Let's talk
Hiring a cybersecurity apprentice for September 2027, or just want to chat? Email or LinkedIn is the easiest. I reply quickly, including from Riga (UTC+2).