
01The project
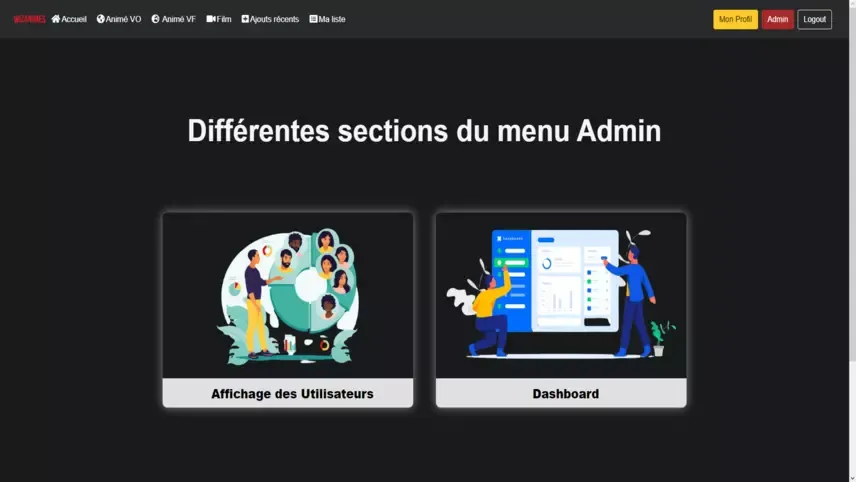
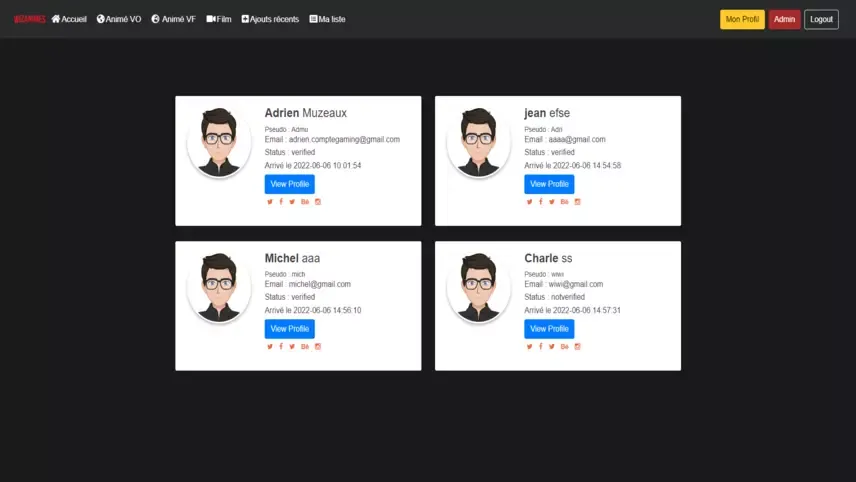
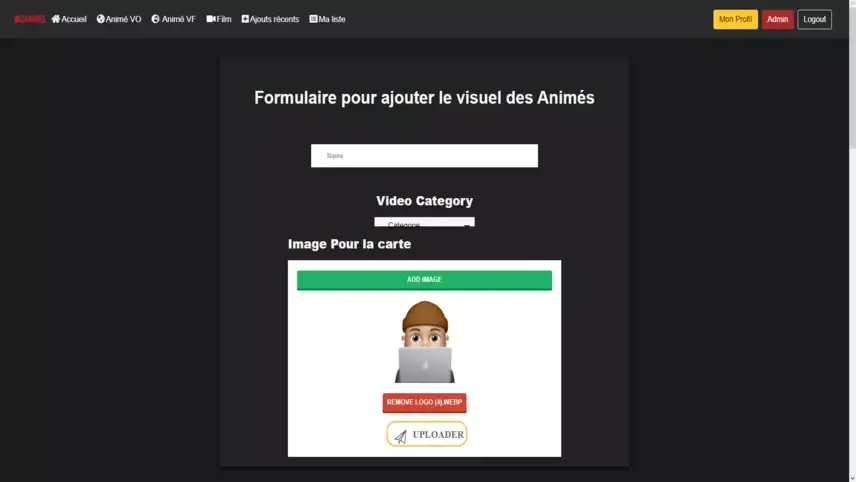
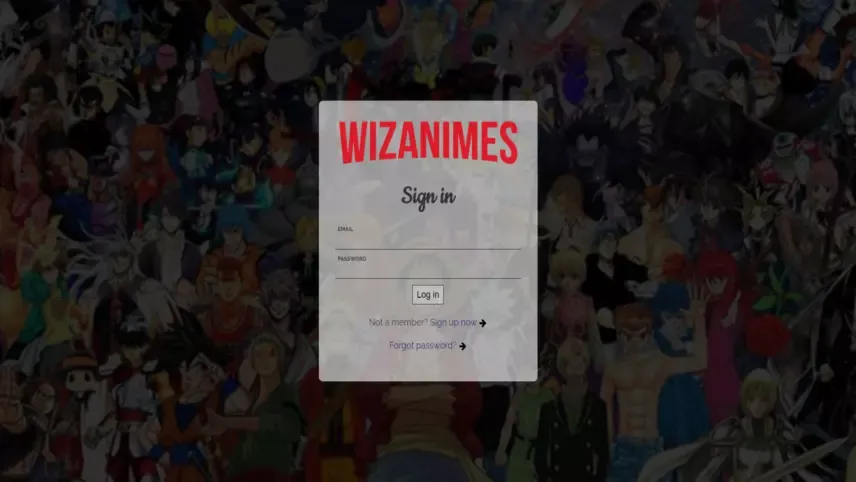
An anime streaming platform I built from scratch in PHP and MySQL in high school: sign-up and login, user profiles, and an admin panel to add series, artwork and video episodes.
Demo video
02Security review, four years later
This is the project that pushed me toward security: an app with accounts, sessions and file uploads is exactly the attack surface you meet in real audits. If I audited it today, here is my checklist:
- SQL injection: do all queries go through prepared statements (PDO)?
- File upload: type checked server-side (not just the extension), stored outside the web root, no way to execute a disguised
.php. - Passwords:
password_hash()/password_verify()instead of a fast hash. - Sessions:
session_regenerate_id()after login,HttpOnly,Secure,SameSitecookies. - CSRF protection on admin actions, and server-side access control on every admin page.
- XSS: systematic escaping (
htmlspecialchars) of user-entered titles and descriptions.
This is not a completed audit: it's the checklist I would apply. Revisiting your own code with an attacker's eye is a great exercise.